
Connect with us


Corporate Video

Agent Development Lifecycle (ADLC): From Use Case to Production AI Agent
An AI agent can look impressive in a demo and still be completely unready for production. A prototype may retrieve the right document, call an API or complete a multi-step task once. Production is different. The agent must work with real business data, interact with real systems, respect permissions, handle failures, control costs and remain observable as models, tools and business requirements change.
That is why organizations need an Agent Development Lifecycle (ADLC) when building production-grade AI systems. Whether you work with an AI agent development company or build agents internally, the lifecycle provides a structured approach to identifying, designing, building, evaluating, deploying, monitoring and improving AI agents throughout their operational life. It helps teams move beyond isolated prototypes toward AI agents that can operate reliably within real business workflows.
There is no universally standardized ADLC framework. IBM describes phases including Plan, Code and Build, Test and Release, Deploy, Operate and Monitor. LangChain describes Build, Test, Deploy and Monitor, while Microsoft describes a lifecycle spanning discovery, experimentation, build, deployment and operational steady state. (IBM)
Despite the different terminology, the underlying principle is consistent: An AI agent should be treated as a continuously engineered production system not a prompt wrapped around an LLM.
What Is the Agent Development Lifecycle (ADLC)?
The Agent Development Lifecycle (ADLC) is a structured, iterative process for developing and operating AI agents from initial use-case identification through production deployment, monitoring, evaluation and continuous improvement.
A practical ADLC can be represented as: Business use case → Architecture → Build → Evaluate → prepare → Deploy → Operate → Improve
The cycle then repeats. This is important because an agent's behavior can depend on its model, instructions, retrieved context, tools, permissions, external systems and runtime state. Changing one of these components can change how the complete workflow behaves.
Microsoft's current agent lifecycle guidance similarly includes versioning, tracing, evaluation, publishing, monitoring and iteration as part of the development process. (Microsoft Learn)
The practical implication is straightforward:
Building the agent is only one part of agent development.
Why Traditional SDLC Is Not Enough for AI Agents
The traditional Software Development Lifecycle (SDLC) remains essential for production AI systems. AI agents still require software architecture, source control, CI/CD, infrastructure, security, API engineering, testing and release management.
However, agents introduce additional variables.
| Dimension | Traditional software | AI agent |
| Behavior | Mostly deterministic | Probabilistic and context-dependent |
| Decision logic | Explicit code | Model reasoning + instructions + tools |
| Data | Usually predefined inputs | May retrieve and interpret changing context |
| Execution | Predefined flow | May select actions dynamically |
| Testing | Functional correctness | Behavioral, task, safety and action evaluation |
| Failure | Bugs, exceptions, infrastructure failures | Wrong reasoning, hallucination, bad retrieval, incorrect tool use or unsafe action |
| Monitoring | Availability, errors, latency | Quality, actions, tool calls, cost, latency, safety and outcomes |
| Changes | Primarily code/configuration | Code, prompts, models, tools, retrieval and policies |
An application might fail visibly because a function throws an error. An agent can fail more subtly: it may successfully call the wrong API, retrieve irrelevant information, make an incorrect assumption or produce a plausible answer that does not solve the task.
That makes evaluation and observability first-class engineering requirements.
The 7 Stages of the AI Agent Development Lifecycle
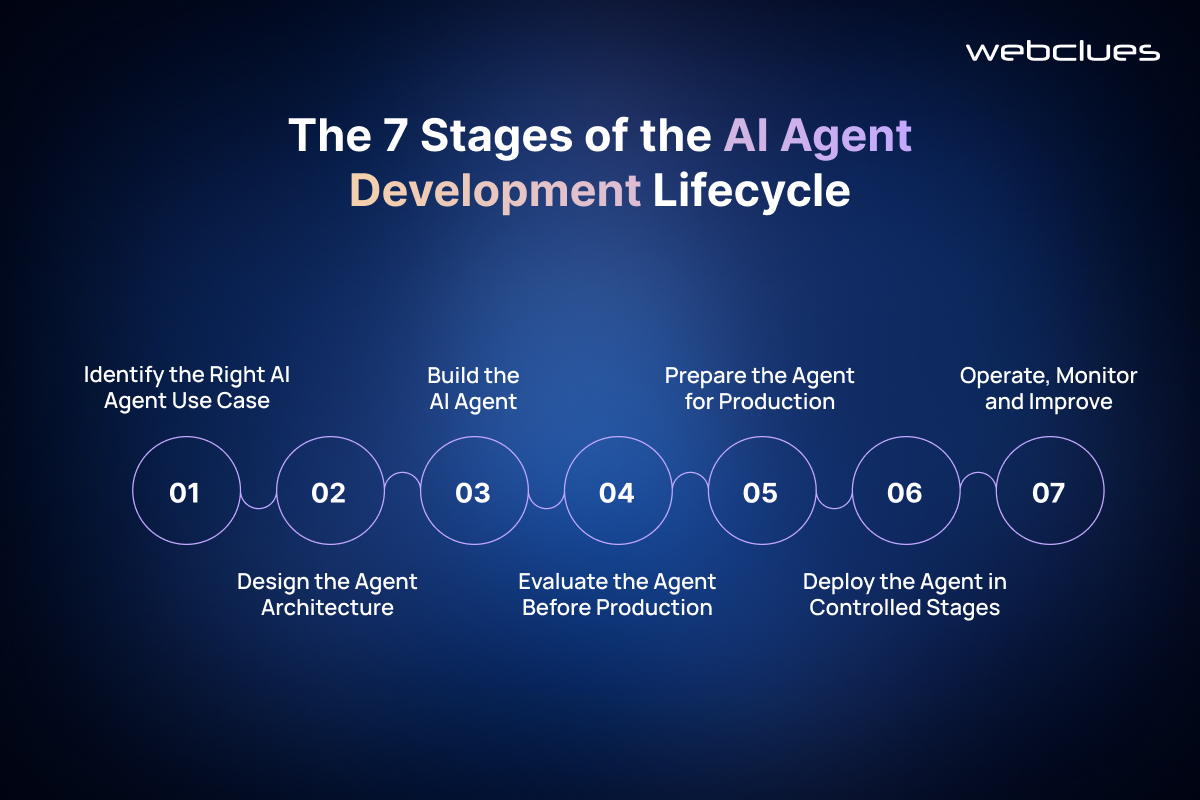
There are several valid ways to divide ADLC into phases. For practical enterprise development, WebClues can frame the lifecycle around seven stages: Identify → Design → Build → Evaluate → prepare → Deploy → Operate & Improve.
Governance, security, observability and evaluation should run across all seven stages rather than being added immediately before production.
1. Identify the Right AI Agent Use Case
The first question should not be:
“Which AI agent framework should we use?”
It should be:
“Does this business problem actually require an agent?”
Agents are most useful when a workflow involves contextual judgment, multiple steps, unstructured information, multiple systems or decisions that cannot be efficiently represented with fixed rules alone.
Potential use cases include:
Customer support investigation and resolution
Internal knowledge workflows
Document-heavy operations
Sales research and qualification
Financial document analysis
IT service management
Procurement workflows
Software engineering assistance
Operations and exception handling
For example, consider customer support.
A conventional automation workflow can route a ticket based on predefined rules. A generative AI application can draft a response. An AI agent may go further by understanding the request, retrieving account information, checking order status, consulting policies, calling approved tools, preparing a response, updating the ticket and escalating when the situation exceeds its authority.
The additional autonomy is useful—but it also creates additional engineering responsibility.
When an AI Agent May Be Unnecessary
Not every AI problem requires an agent.
A deterministic workflow may be better when:
- Rules are stable and explicit.
- There are few meaningful exceptions.
- A conventional API workflow can solve the problem.
- A simple LLM prompt is sufficient.
- Retrieval alone can answer the question.
- The cost and complexity of autonomous execution outweigh the benefit.
The goal is not maximum autonomy.
The goal is the simplest architecture that reliably achieves the required business outcome.
2. Design the Agent Architecture
Once the use case is validated, the next step is to determine how the agent will work.
A production AI agent may contain:
User/Application → Agent Orchestration → LLM → Context/RAG → Tools/APIs → Enterprise Systems
Across these layers sit:
Security + Permissions + Guardrails + Evaluation + Observability
Model Selection
The model is only one architectural decision.
Teams may select different models based on:
- Reasoning requirements
- Context length
- Latency
- Cost
- Domain performance
- Multimodal requirements
- Data residency or deployment constraints
For some workflows, one model may be enough. Others may use different models for planning, extraction, classification, generation or other specialized tasks.
RAG and Context
If an agent needs organization-specific or frequently changing knowledge, retrieval-augmented generation (RAG) may provide access to relevant information without requiring the model to contain that knowledge intrinsically.
But RAG does not automatically make an agent reliable.
The lifecycle should evaluate:
- Retrieval relevance
- Source quality
- Context freshness
- Citation or attribution requirements
- Access controls
- Failure behavior when relevant information cannot be found
Tools and APIs
Tools turn an agent from a conversational system into an action-oriented system.
These tools may include:
- CRM APIs
- ERP systems
- Databases
- Search systems
- Ticketing platforms
- Payment services
- Internal business applications
- File systems
- Analytics platforms
Every tool should have a clearly defined purpose, input schema, permission model, failure behavior and audit path.
3. Build the AI Agent
The build stage converts the architecture into a working system.
This may include:
- System instructions
- Prompt and context design
- Model integration
- Tool calling
- RAG pipelines
- Memory or state management
- Workflow orchestration
- API integration
- Authentication
- Authorization
- Business rules
- Human approval flows
- Logging and tracing
- Error handling
One important principle is to avoid putting every business rule inside the prompt.
Critical constraints should be enforced at the application or tool layer where possible.
For example, an agent may recommend a refund amount, but the payment service should independently verify authorization, transaction status, amount limits and other required conditions before executing the refund.
This creates a separation between:
What the agent proposes
and
What the production system permits.
That separation becomes increasingly important as agents receive access to consequential business operations.
4. Evaluate the Agent Before Production
Testing an AI agent is not simply checking whether its responses “look good.”
The evaluation framework should measure whether the agent accomplishes the intended task safely and consistently.
Quality Metrics
Depending on the use case, evaluate:
- Task completion rate
- Accuracy
- Groundedness
- Retrieval relevance
- Tool-call success
- Instruction adherence
- Correct escalation
Safety Metrics
Evaluate:
- Policy violations
- Unauthorized actions
- Sensitive-data exposure
- Prompt injection resistance
- Unsafe tool use
- Access-control failures
Agent security has become a distinct concern because agents can combine model-generated decisions with access to tools and external systems. OWASP's Agentic AI guidance identifies risks including goal hijacking, tool misuse, identity and privilege abuse, supply-chain vulnerabilities and unexpected code execution. (OWASP Gen AI Security Project)
Operational Metrics
Measure:
- Latency
- Token consumption
- Cost per task
- Tool latency
- Failure rate
- Retry frequency
- Human handoff rate
Business Metrics
The most important metrics often sit outside the model itself.
Depending on the workflow, these may include:
- Resolution time
- Cost per completed case
- Employee time saved
- Customer satisfaction
- Conversion rate
- Exception rate
- Revenue generated or protected
Offline and Online Evaluation
A strong ADLC uses both.
Offline evaluations run the agent against a controlled dataset before release. They help compare prompts, models, tools, retrieval strategies and architecture changes.
Online evaluations analyze production behavior after deployment. They can identify quality degradation, emerging failure patterns, tool problems and changes in user feedback.
LangChain's current ADLC guidance explicitly distinguishes offline evaluations from online evaluations and recommends using production traces to strengthen future test datasets. (LangChain)
The result is a feedback loop:
Production failure → Evaluation case → Experiment → Regression test → New release
5. Prepare the Agent for Production
An agent that performs well in testing may still not be ready for production.
Production prepareing addresses the gap between functional and operationally safe.
Important controls include:
Least-Privilege Access
An agent should receive only the data and tools required for its assigned workflow.
NIST's 2026 work on AI-agent identity and authorization specifically highlights the need to address identification, authorization, auditing and non-repudiation as agents gain access to data, tools and applications. (NIST Computer Security Resource Center)
Human-in-the-Loop
High-impact operations may require human approval.
Examples include:
Financial transactions
Contract changes
Account closure
Sensitive customer actions
Production infrastructure changes
High-value refunds
Human approval should be part of the architecture, not an emergency fallback added after deployment.
Failure Handling
Production agents need explicit behavior for:
- API timeouts
- Rate limits
- Invalid tool responses
- Missing information
- Conflicting data
- Authentication failures
- Partial workflow completion
- Duplicate requests
For state-changing operations, duplicate protection and idempotency should be considered wherever supported by the downstream system.
Sandboxing
Agents that execute code, manipulate files or operate in potentially risky environments may require isolated execution environments.
The purpose is to reduce the potential impact of incorrect or malicious behavior by limiting access to compute, storage, networks and system resources.
6. Deploy the Agent in Controlled Stages
Deployment is not the point at which development ends.
It is the beginning of production validation.
A controlled rollout may progress through:
Development → Staging → Internal Users → Limited Production → Wider Production
Depending on the application, teams can use:
- Feature flags
- Canary releases
- Limited user cohorts
- Shadow testing
- Rate limits
- Permission restrictions
- Rollback procedures
Versioning is equally important.
An agent's behavior may depend on:
- Model version
- Prompt version
- Tool definitions
- RAG configuration
- System policies
- Application code
- Agent workflow
- Evaluation configuration
Microsoft Foundry's current lifecycle guidance, for example, emphasizes immutable agent versions, tracing, repeatable evaluations, publishing and controlled updates.
A production team should be able to answer:
Which version of the agent produced this action?
7. Operate, Monitor and Improve
Deployment does not complete the ADLC.
It starts the most important feedback loop.
An agent may encounter real-world combinations that were not represented in pre-production tests. Users may phrase requests differently. Data may change. APIs may become slower. A model update may alter tool-selection behavior.
Monitoring therefore needs to cover more than uptime.
What to Monitor in Production
Track:
- Task success
- User feedback
- Accuracy
- Tool-call failures
- Retrieval quality
- Latency
- Token usage
- Cost
- Escalation rates
- Safety events
- Policy violations
- Error patterns
- Model or workflow regressions
Why Agent Tracing Matters
A traditional application log may tell you that a request failed.
An agent trace should help answer:
- What did the user ask?
- What context was retrieved?
- Which model was used?
- Which tools were selected?
- What parameters were sent?
- What did each tool return?
- Where did the workflow deviate?
- What was the final outcome?
Microsoft and LangChain both emphasize tracing as an important mechanism for understanding agent behavior and improving agents after deployment.
The operational loop should therefore look like:
Trace → Diagnose → Change → Evaluate → Deploy → Monitor
This is what turns an experimental AI agent into an engineered production system.
AI Agent Lifecycle Management and Governance
Governance should not be treated as a final checklist. It should exist throughout the lifecycle. An enterprise agent inventory should ideally track:
- Agent owner
- Business purpose
- Environment
- Version
- Model
- Connected tools
- Data sources
- Permissions
- Risk classification
- Evaluation status
- Deployment status
- Usage
- Cost
- Incident history
- Retirement status
As organizations move from one or two agents to dozens or hundreds, discoverability and reuse become increasingly important.
Teams may otherwise create multiple agents that perform overlapping tasks, use different policies, duplicate integrations or consume resources without centralized visibility.
Governance should also cover cost. Agent workloads can involve multiple model calls, retrieval operations, tool calls, retries and long-running workflows. Cost controls therefore need to operate at the agent, team, application, model or workflow level where appropriate.
The objective of governance is not to prevent experimentation. It is to make experimentation possible without losing control.
Single-Agent vs. Multi-Agent Development
Not every workflow requires multiple agents.
A single agent is often easier to:
- Build
- Evaluate
- Monitor
- Debug
- Secure
- Operate
A multi-agent architecture can be appropriate when the workflow contains genuinely distinct responsibilities that benefit from specialization.
For example:
Coordinator Agent → Research Agent → Analysis Agent → Compliance Agent → Human Reviewer
But each additional agent creates another interface, state boundary, failure point and evaluation surface.
Before introducing multi-agent orchestration, ask whether the same workflow can be handled reliably by:
One agent + deterministic workflow logic + well-designed tools.
Complexity should be justified by measurable value.
AI Agent Development Lifecycle Checklist
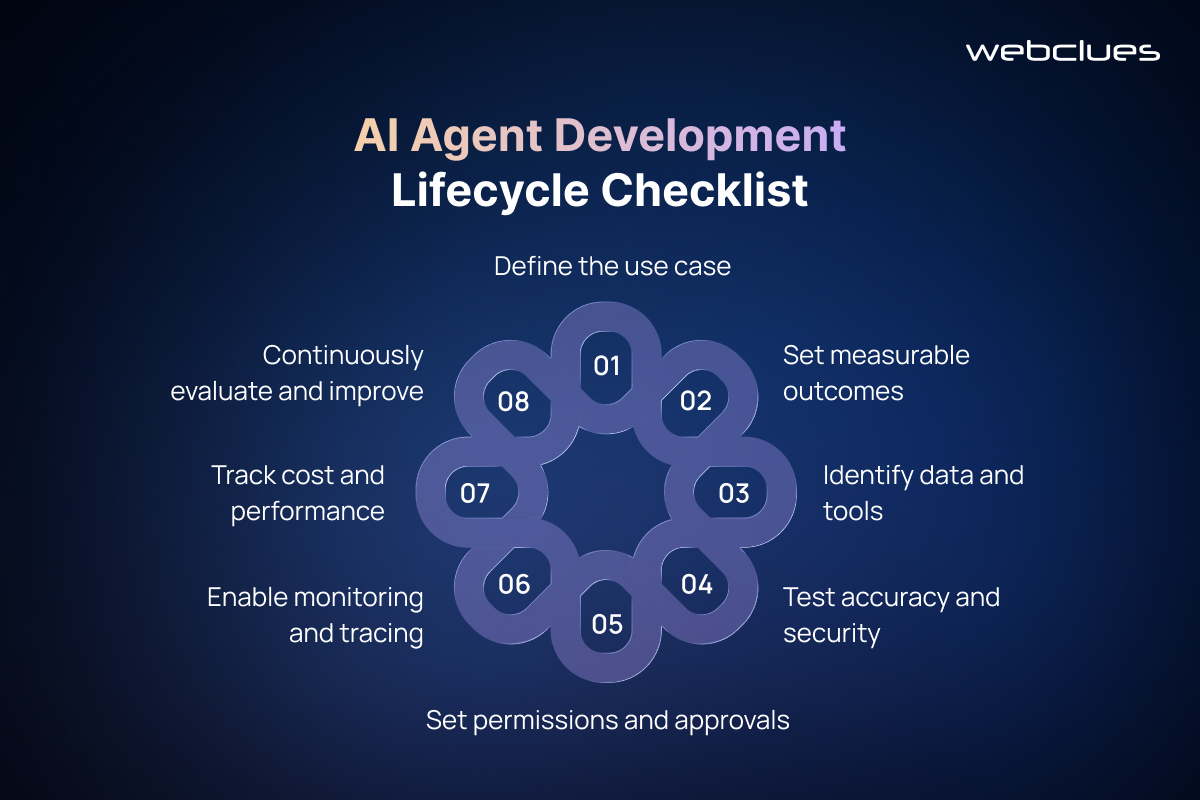
Use this checklist before moving an agent toward production.
Before Building
- Business problem is clearly defined
- Agentic architecture is justified
- Business outcome is measurable
- Required data sources are identified
- Required tools and APIs are identified
- Human approval points are defined
- Risk and permission boundaries are documented
Before Production
- Representative evaluation dataset exists
- Edge cases have been tested
- Tool calls have been evaluated
- Security testing is complete
- Prompt-injection scenarios have been considered
- Permissions follow least privilege
- Human escalation is implemented
- Tracing and observability are enabled
- Cost and latency have been measured
- Rollback procedures are defined
After Deployment
- Production quality is monitored
- User feedback is captured
- Agent traces are reviewed
- Failures become regression cases
- Model and prompt changes are evaluated
- Tool failures are monitored
- Cost is tracked
- Governance reviews continue
- Outdated agents are retired or updated
How WebClues Infotech Helps Build Production AI Agents
Moving from an AI-agent concept to a production system requires more than selecting an LLM. It requires business workflow analysis, architecture, data engineering, integrations, agent orchestration, evaluation, security, deployment and ongoing optimization.
WebClues Infotech's AI development services cover AI agent and copilot development, generative AI, LLM and RAG development, tool and function calling, multi-agent systems, enterprise integrations, testing, deployment and post-deployment improvement.
The development approach starts with the actual use case and evaluates whether AI is the appropriate solution before selecting an architecture. This can help avoid overengineering a workflow simply because agentic AI is available.
For organizations moving beyond experimentation, the focus should be on building an agent that can operate within the realities of existing business systems.
That means connecting the agent to the right data and applications, defining what it can and cannot do, evaluating behavior against realistic scenarios and establishing monitoring for the production environment.
WebClues also provides AI integration capabilities for connecting AI systems with existing enterprise applications, APIs, data and workflows rather than requiring organizations to replace their existing software stack.
The result is a development process focused on moving from:
Use case → Prototype → Evaluated agent → Production integration → Controlled deployment → Continuous improvement
Final Thoughts
The hardest part of AI agent development is rarely getting an agent to work once.
The harder problem is getting it to work reliably, securely, measurably and repeatedly in a real business environment.
The Agent Development Lifecycle begins with the business problem rather than the model. It validates whether an agent is appropriate, designs the required architecture, builds the necessary tools and context, evaluates behavior, establishes production controls, deploys gradually and continuously learns from real-world usage.
The most important shift is conceptual: Production deployment is not the end of AI agent development. It is the start of the operational feedback loop.
When every production failure can become an evaluation case, every meaningful change can be tested and every consequential action can be governed and traced organizations can move from isolated AI-agent experiments toward repeatable production systems.
That is where ADLC becomes more than a development methodology. It becomes an operating discipline for building AI agents that can deliver measurable business value while remaining observable, controlled and adaptable over time.
Ready to move an AI agent from prototype to production? Explore WebClues Infotech's AI agent development services or discuss your AI use case with the WebClues team.
Post Author
Ayush Kanodia
As one of the esteemed Directors of WebClues Infotech. Ayush Kanodia is passionate about delivering innovative IT services & solutions and has spearheaded numerous successful projects, cementing the company's position as a leader in the field.


Build Your Agile Team
Hire Skilled Developer From Us
Move Your AI Agent From Prototype to Production
Build production-ready AI agents with the right architecture, tools, RAG, security controls, evaluation, and observability. Explore WebClues Infotech’s AI agent development services for enterprise workflows and real-world use cases.
Connect Now!Frequently Asked Questions
Our Recent Blogs
Sharing knowledge helps us grow, stay motivated and stay on-track with frontier technological and design concepts. Developers and business innovators, customers and employees - our events are all about you.