
Connect with us


Corporate Video

How to Build an Autonomous AI Agent from Scratch in 2026
Building an autonomous AI agent in 2026 is technically easier than it was a few years ago. Models can reason over complex instructions, call tools, work with external data, maintain state, and coordinate multiple steps. But putting an LLM into a loop does not automatically create a production-ready autonomous agent.
Where should the agent be autonomous, and where should the system remain deterministic? A reliable AI agent needs a defined business goal, appropriate model, tools, context, memory, execution limits, security controls, evaluation, and observability.
The most effective architecture is often a hybrid: let the agent make decisions where flexibility matters, while using conventional software controls where predictability matters.
This guide explains how to build an autonomous AI agent from scratch in 2026, from defining the use case and selecting an architecture to integrating tools, implementing guardrails, testing performance, and preparing the system for production.
If you are considering partnering with an AI agent development company for implementation, these principles can also help you evaluate the right technical approach.
What Is an Autonomous AI Agent?
An autonomous AI agent is a software system that can pursue a defined goal by deciding which actions to take, using available tools, observing the results, and determining what to do next.
This is different from a conventional chatbot. A chatbot generally responds to an input. An agent can take a goal such as “investigate this customer issue,” retrieve information, call business APIs, evaluate the results, perform an approved action, and continue until it reaches a defined outcome or needs human intervention.
Anthropic distinguishes between workflows, where predefined code controls the sequence, and agents, where the model dynamically directs its own process and tool usage. It also recommends using the simplest architecture that can reliably solve the problem.
AI Agent vs. Chatbot vs. AI Workflow
| System | How it operates | Example |
| Chatbot | Generates a response | Answers an order-status question |
| AI workflow | Follows predefined steps | Checks order → retrieves status → sends response |
| AI agent | Dynamically chooses actions | Investigates the issue → checks multiple systems → decides next step |
The distinction matters because many projects described as “autonomous AI agents” do not actually require open-ended autonomy. AI workflow automation may be safer, cheaper, and easier to maintain.
What Does “Autonomous” Actually Mean?
Autonomy should not mean unrestricted access or the absence of human oversight. A production agent should operate within defined boundaries. Those boundaries can include which tools it can call, what data it can access, how many actions it can take, which decisions require approval, and when execution must stop. The objective is therefore not maximum autonomy. It is appropriate autonomy.
What Makes an AI Agent Truly Autonomous?
An autonomous AI agent requires more than an LLM and a prompt. It needs several connected components that allow it to reason, act, observe and adjust.
A Goal the Agent Can Act On
The goal should describe an outcome rather than simply an instruction to generate text. For example, “answer customer questions” is broad. “Resolve eligible order-status requests using the order management system and escalate exceptions” gives the agent a defined objective.
A Reasoning Model
The LLM acts as the reasoning engine. It interprets the task, evaluates available information, selects an action and determines whether another step is required. Model selection should consider reasoning quality, tool-use reliability, latency, context requirements, privacy requirements and operating cost.
Tools That Can Change the Environment
Tools allow the agent to move beyond generating text. Depending on the use case, these can include APIs, databases, search, CRM systems, ticketing platforms, code execution or other business applications. Current agent SDKs support function tools, hosted tools, MCP-based integrations and agents-as-tools patterns.
State, Context and Memory
The agent needs enough context to understand what has already happened. Working state can track the current task, while longer-term memory can retain information across interactions where that is genuinely useful. Memory should be designed around the use case rather than added automatically.
A Decision-and-Execution Loop
The core pattern is: Goal → Reason → Act → Observe → Decide → Repeat
The agent uses the result of each action to determine the next step.
Clear Stop Conditions
Autonomous execution should have explicit boundaries, such as:
- Task completed
- Maximum number of iterations reached
- Tool failure
- Confidence or validation threshold not met
- Cost or token limit reached
- Human approval required
Without stop conditions, an agent can continue making unnecessary tool calls or repeatedly attempt a failing action.
What You Need Before Building an Autonomous AI Agent
The most important development work often happens before writing the first line of agent code.
Define the Business Outcome
Start with the process you want to improve.
Instead of: “We need an AI sales agent.”
Define: “The system should research inbound leads, enrich company information, score them against defined criteria and prepare a CRM update for approval.”
The second version gives engineers something measurable to build.
Define What the Agent Is Allowed to Do
Create an explicit action boundary. For example, a support agent may be allowed to retrieve customer records and update ticket status but require approval before issuing a refund.
Identify the Systems It Must Access
Map every required source and destination:
- CRM
- ERP
- Databases
- Internal knowledge bases
- Ticketing systems
- Communication platforms
- Payment systems
- Third-party APIs
This determines much of the eventual AI agent development process.
Define Success and Failure
Decide how the system will be evaluated before deployment. Useful measures can include task completion, tool-call accuracy, escalation rate, latency, cost per task and business-specific KPIs.
Decide Where Humans Stay in the Loop
Human approval is not a failure of autonomy. For high-impact actions, it can be an intentional control.
How to Build an Autonomous AI Agent from Scratch
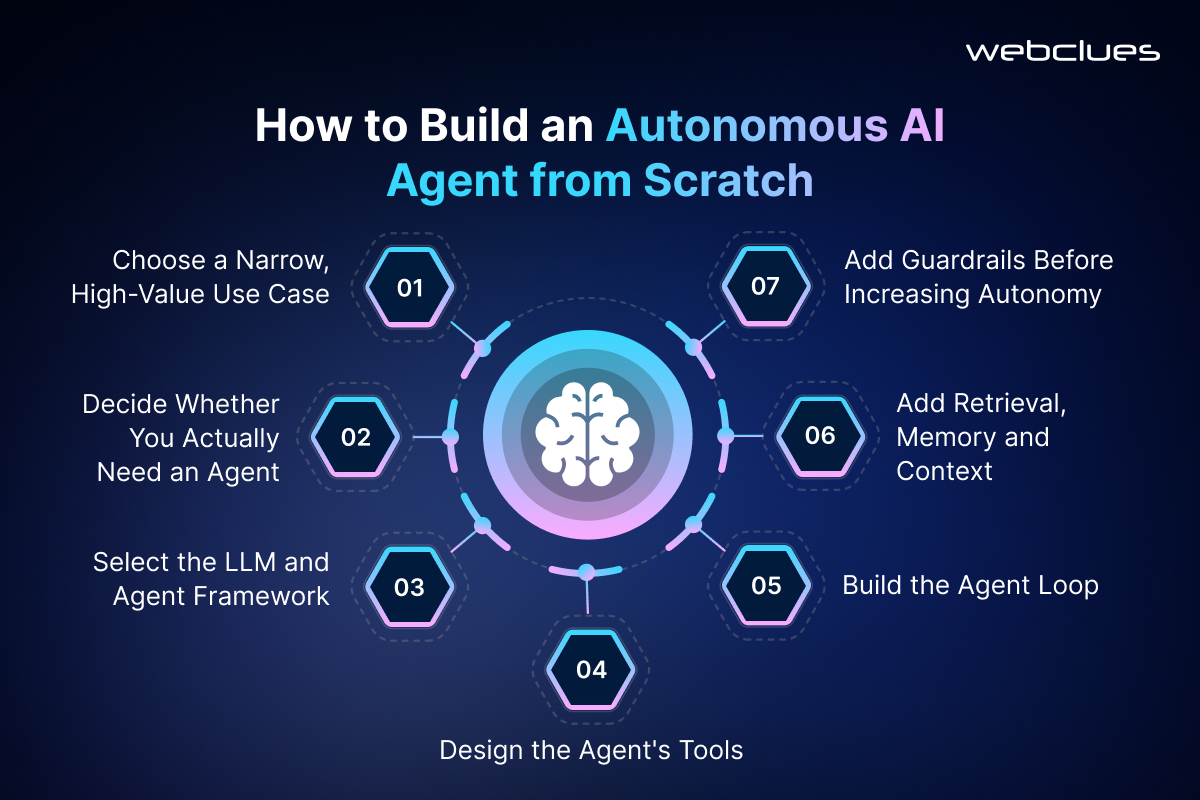
Building an autonomous AI agent starts with a clear business goal, then progressively adds reasoning, tools, memory, safeguards, and evaluation to create controlled autonomy.
Step 1: Choose a Narrow, High-Value Use Case
Start with one workflow where agentic decision-making can create measurable value. A narrow use case also makes evaluation easier. Once the system performs reliably, additional workflows can be introduced.
Step 2: Decide Whether You Actually Need an Agent
This is one of the most important architecture decisions. Use a conventional workflow when the steps are predictable. Use an agent when the system must dynamically determine what to do based on changing inputs.
For many enterprise applications, the right answer is a hybrid. Anthropic recommends starting with the simplest solution and increasing agentic complexity only when it produces a meaningful improvement in results. Agents can also trade additional latency and cost for greater flexibility.
Step 3: Select the LLM and Agent Framework
Evaluate models based on the actual workload rather than benchmark reputation alone. Consider:
- Reasoning performance
- Tool calling
- Context handling
- Latency
- Cost
- Data requirements
- Provider ecosystem
Frameworks can simplify orchestration, tool execution, guardrails and state management. For example, the OpenAI Agents SDK provides agents, tools, guardrails, handoffs, sessions, human-in-the-loop capabilities and tracing.
However, a framework should not dictate the architecture. Understand what happens underneath the abstraction so the system remains debuggable.
Step 4: Design the Agent's Tools
A tool is an interface between the agent and the outside world. Each tool should have a clearly defined purpose, structured inputs, validated outputs and appropriate permissions. Consider:
- Authentication
- Input validation
- Output validation
- Timeouts
- Retry rules
- Error handling
- Permission scope
Destructive-action controls
The tool interface effectively becomes part of the agent's operating environment, so poor tool definitions can produce poor agent behavior.
Step 5: Build the Agent Loop
The basic execution flow is:
Receive goal
↓
Inspect context
↓
Decide next action
↓
Call tool
↓
Observe result
↓
Validate result
↓
Continue, escalate, or stop
Modern agent runtimes can manage parts of this loop automatically. For example, OpenAI's Agents SDK uses a runner to manage agent turns, tool calls and related execution behavior.
Step 6: Add Retrieval, Memory and Context
Retrieval gives the agent access to relevant external information. Memory can preserve useful information across turns or tasks. But more context is not automatically better.
Anthropic's current guidance describes context engineering as the process of continuously curating what information enters the model's context during multi-step agent execution. The goal is to provide the right context at the right step, not everything available.
Step 7: Add Guardrails Before Increasing Autonomy
Implement validation and permissions before giving the agent additional capabilities. Guardrails can check inputs, outputs and tool calls. OpenAI's Agents SDK, for example, supports input, output and tool guardrails that can validate or block execution.
How to Choose the Right Agent Architecture
There is no universal “best” AI agent architecture. The right choice depends on task variability, risk, integrations and the amount of decision-making required.
Single-Agent Architecture
A single agent is suitable when one reasoning system can manage the task and its tools without excessive complexity. It is usually easier to test, monitor and maintain.
Multi-Agent Architecture
A multi-agent system separates responsibilities among specialized agents.
For example:
Research agent → Analysis agent → Compliance agent → Execution agent
This can help when different tasks require different instructions or capabilities. But every additional agent also introduces orchestration, communication and evaluation complexity. OpenAI's current Agents SDK supports both manager-style “agents as tools” and handoff patterns for multi-agent systems.
Workflow + Agent Hybrid Architecture
For many enterprise applications, this is the most practical approach.
Use deterministic software for:
- Authentication
- Validation
- Compliance rules
- Financial limits
- Required approvals
- Mandatory business logic
Use agentic reasoning for:
- Research
- Classification
- Planning
- Selecting among valid actions
- Handling variable inputs
This approach provides flexibility without handing every business decision to a model.
How to Decide Between Workflow, Hybrid and Autonomous Agent
A simple rule is:
Predictable process → workflow
Variable decisions inside a controlled process → hybrid
Open-ended, multi-step task with measurable outcomes → agent
This architecture-first approach can prevent organizations from paying for unnecessary agentic complexity.
How to Add Tools, Memory and Business Data
Connecting the right tools, business data, and memory gives an AI agent the context and capabilities it needs to take useful actions reliably.
Connect APIs and Enterprise Systems
An agent becomes operationally useful when it can work with the systems where business information and actions actually reside. API integrations can allow an agent to retrieve customer information, update records, create tickets, search inventory or trigger approved workflows.
Use Retrieval for Current Business Knowledge
RAG and other retrieval mechanisms can provide access to current internal information without embedding every piece of knowledge directly into the model. The retrieval layer should still be evaluated for relevance, access control and freshness.
Design Memory Around the Task
Ask what information genuinely needs to persist. A support agent may need customer and conversation context. A one-time document-processing agent may need no long-term memory at all.
Introduce MCP Where It Makes Sense
Model Context Protocol can provide a standardized way to connect models and agents with external tools and data sources. It can be useful where multiple tools or integrations need a consistent interface. It should still be treated as an architectural choice, not a mandatory component of every AI agent.
Control Tool Permissions
A tool that can read a customer record should not automatically have permission to modify it. Separate read and write capabilities where appropriate and apply least-privilege access to every connected system.
How to Make an Autonomous AI Agent Reliable and Secure
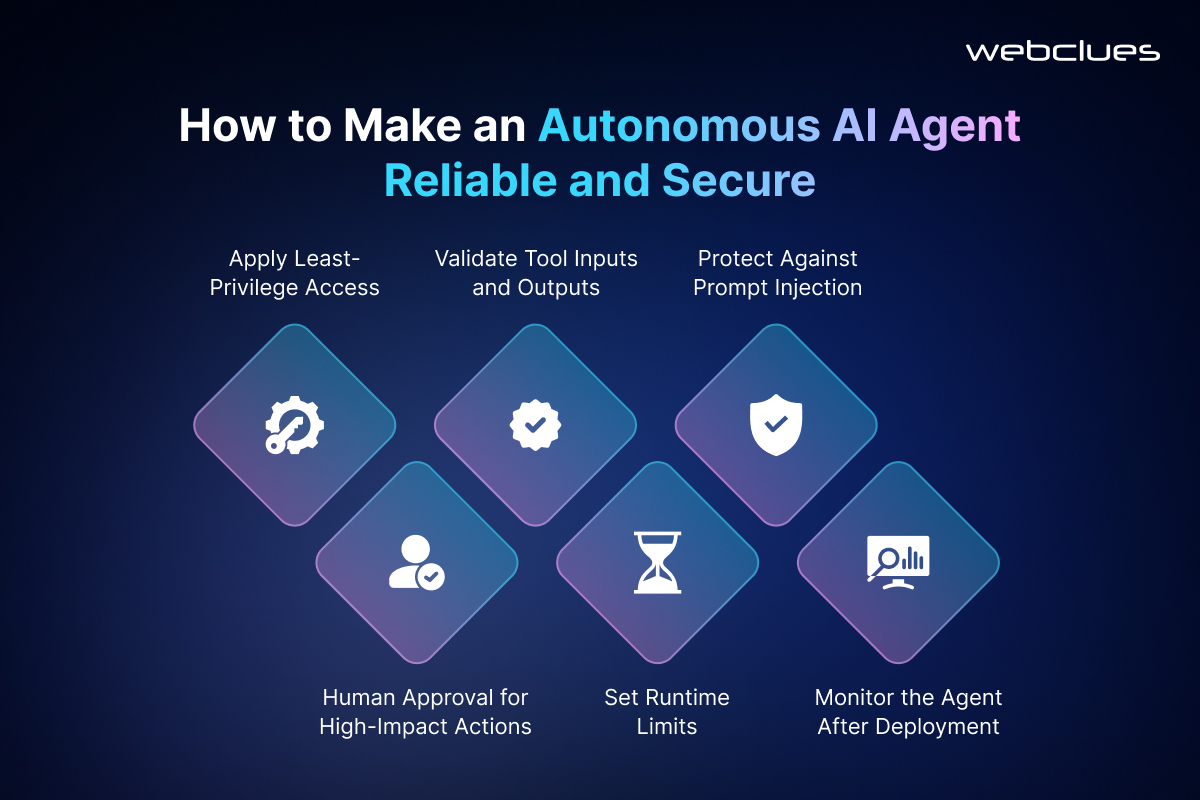
Autonomy increases the importance of security because an agent can potentially turn model decisions into real-world actions.
OWASP's 2026 Top 10 for Agentic Applications is specifically focused on security risks affecting autonomous and agentic AI systems and was developed with input from more than 100 industry experts, researchers and practitioners.
Apply Least-Privilege Access
Give the agent only the permissions required to complete its assigned task.
Validate Tool Inputs and Outputs
Never assume that model-generated parameters are safe or valid. Validate them before execution and validate important tool results before they are passed into subsequent decisions.
Protect Against Prompt Injection
External content can contain instructions that conflict with the agent's actual objective. Retrieved content should therefore be treated as data, not automatically as trusted instructions.
Add Human Approval for High-Impact Actions
Approval gates are appropriate for actions such as:
- Financial transactions
- Account deletion
- Sensitive data changes
- Contractual actions
- Production changes
- High-value customer decisions
Set Runtime Limits
Use limits for:
- Maximum iterations
- Tool-call frequency
- Execution time
- Cost
- Retry attempts
Monitor the Agent After Deployment
Observability should cover the complete execution path, including model calls, tool calls, handoffs, guardrails, failures and latency. OpenAI's Agents SDK includes tracing that records agent execution events and can be used to debug and monitor workflows.
How to Test and Evaluate an AI Agent
Testing an autonomous agent requires more than checking whether its final answer sounds correct.
Test Normal Business Scenarios
Build an evaluation set based on realistic production tasks.
Test Tool Selection and Parameters
Check whether the agent selects the correct tool and supplies valid arguments.
Test Failure and Recovery
Deliberately introduce:
- API failures
- Missing data
- Invalid responses
- Timeouts
- Conflicting information
- Incorrect tool results
The agent should recover, escalate or stop rather than continue blindly.
Test Adversarial Inputs
Include prompt injection, malicious instructions, unauthorized requests and attempts to bypass tool permissions.
Measure Business Outcomes
Track metrics that matter to the organization, such as:
- Task completion
- Accuracy
- Escalation rate
- Cost per task
- Latency
- Human intervention
- Business KPI improvement
Create an Evaluation Loop
The production cycle should be:
Test → Observe → Identify failure → Adjust → Retest → Deploy
Agent development does not end when the first version works. Evaluation and iteration are part of the operating model.
How Much Does AI Agent Development Cost?
There is no single price for AI agent development because the engineering scope varies substantially between a small internal assistant and an enterprise system connected to multiple operational platforms.
What Determines AI Agent Development Cost?
Major AI agent cost drivers include:
- Use-case complexity
- Model selection and usage
- Number of tools
- API integrations
- Data and retrieval requirements
- Memory requirements
- Security controls
- Human approval workflows
- User interface
- Infrastructure
- Monitoring
- Maintenance and optimization
An agent that reads information from one API is fundamentally different from an agent that coordinates several enterprise systems and can perform consequential actions.
Prototype vs. Production AI Agent Cost
A prototype may demonstrate that an agent can reason and call a tool.
A production system also needs:
- Authentication
- Permission management
- Error handling
- Evaluation
- Observability
- Security testing
- Scalability
- Maintenance
That is why an AI agent development cost estimate should be based on the required architecture and operational scope rather than simply the number of prompts or screens.
How to Estimate Your AI Agent Development Budget
Before requesting an estimate, define:
- The business process being automated
- The decisions the agent must make
- The systems it must access
- The actions it can perform
- The data it requires
- Human approval requirements
- Security and compliance requirements
- Expected workload
- Success metrics
- Ongoing monitoring and maintenance needs
This produces a much more useful scope for custom AI agent development.
When Should You Work With an AI Agent Development Company?
Building an initial prototype internally can make sense when the use case is narrow and the organization has experienced AI engineers.
External AI agent development services become more valuable when the system must integrate with multiple enterprise platforms, operate securely in production, or move beyond experimentation.
Build In-House When
An internal approach can be appropriate when:
The use case is narrow
AI engineering expertise already exists
Integrations are manageable
The team can own evaluation and maintenance
The organization wants complete control of the implementation
Use AI Agent Development Services When
AI Agent development partner can be useful when:
Multiple business systems must be integrated
Production security is important
Internal agent engineering expertise is limited
A PoC needs to become a production system
Ongoing evaluation and optimization are required
The business needs additional engineering capacity
What to Look for in an AI Agent Development Company
Do not evaluate vendors only on whether they can demonstrate a chatbot.
Look for experience with:
- Agent architecture
- LLM integration
- Tool calling
- RAG
- API integration
- Agent orchestration
- Guardrails
- Evaluation
- Observability
- Security
- Deployment
- Ongoing maintenance
The right AI agent development partner should be able to explain why a particular architecture is appropriate, not simply recommend the most complex one.
Build Your Autonomous AI Agent With WebClues
Autonomous AI agents can automate complex, multi-step work, but successful implementation depends on more than selecting an LLM. The architecture needs to connect business goals with the right level of autonomy, tools, data, permissions, evaluation and human oversight.
WebClues Infotech provides AI development capabilities for startups, enterprises and growth-stage teams, with AI development among its areas of expertise.
If you have a workflow that requires dynamic decision-making, tool use and multi-step execution, WebClues can help translate that requirement into an appropriate agent architecture and production implementation.
Ready to build an AI agent around your actual business workflow? Connect now with the WebClues team to learn more about AI Agent Development Services and discuss your use case.
Post Author
Ayush Kanodia
As one of the esteemed Directors of WebClues Infotech. Ayush Kanodia is passionate about delivering innovative IT services & solutions and has spearheaded numerous successful projects, cementing the company's position as a leader in the field.


Build Your Agile Team
Hire Skilled Developer From Us
Build a Working AI Agent for Your Business
Turn complex workflows into reliable AI agents with the right architecture, integrations, and safeguards. WebClues can help you move from AI agent consulting to custom development and implementation. Ready to explore your use case? Talk to our team.
Connect Now!Frequently Asked Questions
Our Recent Blogs
Sharing knowledge helps us grow, stay motivated and stay on-track with frontier technological and design concepts. Developers and business innovators, customers and employees - our events are all about you.